Steam API scams: how trade impersonation works
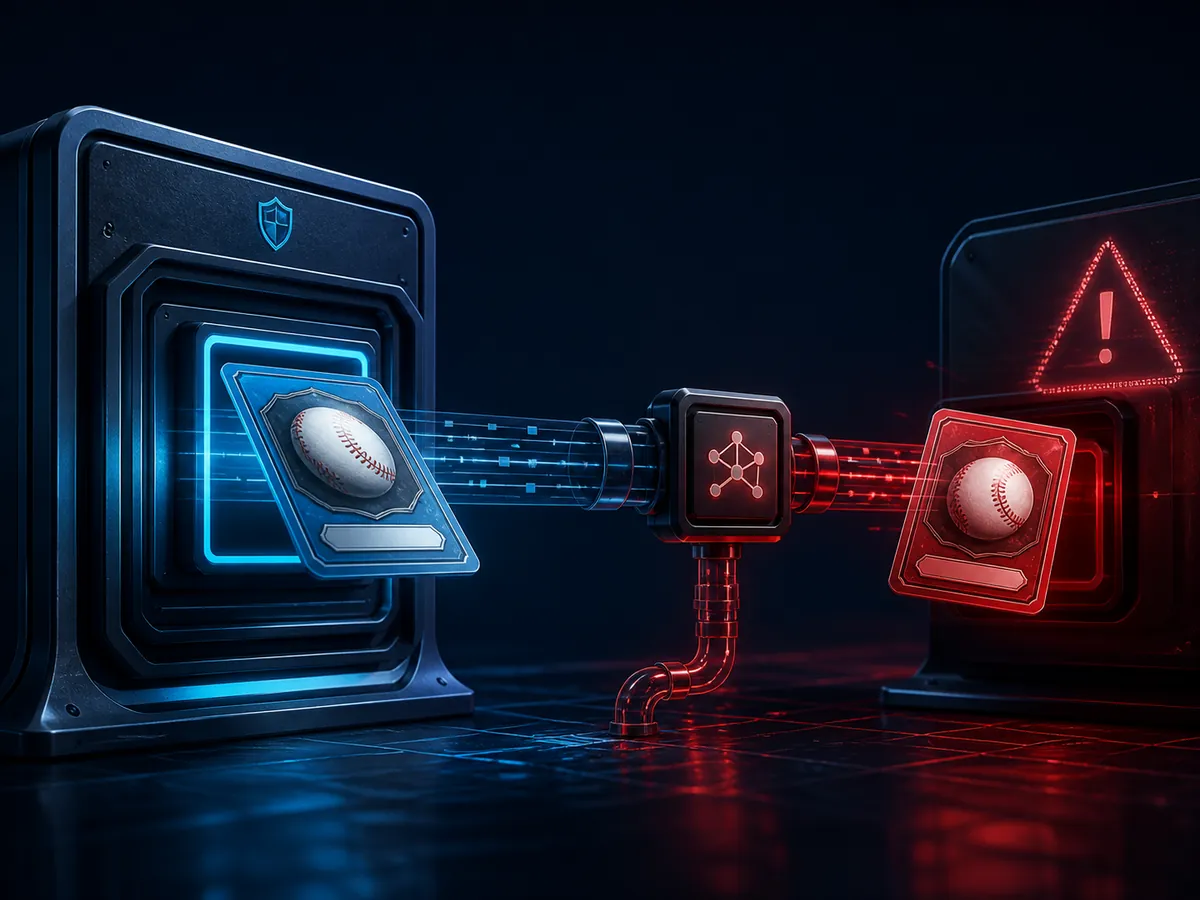
API scam is the most unpleasant scheme in trading, because the moment you notice it, a stranger already has access to your account. Let's look at what exactly is happening, because there are more myths than facts surrounding this scheme.
A complete analysis of the scheme from the inside: what is really happening, why deleting the key is not enough, and in what order to save the account.
What actually happens
First, the attacker gains access to the account. Through a phishing login page, malware on your computer, or a stolen session - the method is not important, the fact itself is important.
Next, he registers a Web API key on your account and sets up automation that monitors your trade offers.
You start a regular trade. The automation instantly cancels your real offer and creates a visually identical one - with the same items, the same nickname and avatar, but from a fake account.
You see a familiar offer, think “it fell off, came again,” and confirm it in the mobile application. Items go the wrong way.
Key detail: Steam is not hacked. You did all the confirmation yourself, with your authenticator. This is why it is almost impossible to return items.
Why the name is misleading
Because of the word “API,” many people believe that the problem is in the key and that it is enough to delete it. This is not true, and it is a dangerous misconception.
The key is simply a convenient automation tool. Anyone who has full access to the account will do the same without it, manually. And it will create a new key a minute after you delete the old one.
The real problem is account or device compromise. Until it is eliminated, any actions with the key are meaningless.
Signs of account compromise
There is a key on the page steamcommunity.com/dev/apikey that you did not create.
An trade offer is canceled and a similar one comes immediately - especially if this is repeated.
In the security settings, active sessions from unfamiliar devices or from other cities are visible.
There are letters in the mail about logging in that you did not sign up for, or letters about changing settings.
There are transactions in the history of exchanges that you do not remember.
Steps to secure the account
Consistency is more important than speed here - if you do it out of order, everything will have to be repeated.
First: stop all current operations and leave the infected device. Then work from your phone or someone else’s clean computer.
Second: check your computer with an antivirus. If there is malware, it is useless to change passwords from it - the new password will leak in the same way as the old one.
Third: change the password of the mail to which Steam is linked. Access is restored through her, so she is the first.
Fourth: change the password Steam and end all active sessions in the security settings.
Fifth: revoke the Web API key. Only now, when access is already closed.
Sixth: check your trade history, active offers and settings to see if there are any new bindings.
- Do not tell the Steam Guard recovery code to anyone, including those who pretend to be support.
- Do not continue communication with the person with whom the transaction was made.
- Save links to profiles, screenshots and exchange numbers before contacting support.
Prevention
The only reliable protection is not to give away access. Visit the sites using your bookmarks, and not via links from messages. Do not enter Steam data on pages that open themselves. Do not run programs sent in a personal message, even from friends.
And a habit that catches the scheme at the last step: in mobile confirmation, always look at the partner’s permanent SteamID, and not at the nickname and avatar. If an offer is canceled and a new one comes, stop and check from scratch. It is at this moment that the scheme works.
Frequently asked questions
What is API scam in simple words?
A scheme in which an attacker with access to your account replaces the trade offer with one visually identical to his profile, and you confirm it yourself.
Is it enough to delete the API key?
No. The key is the tool, not the cause. While the account or device is compromised, a new key will be created again.
Can the exchange change after my confirmation?
No. The substitution occurs before confirmation - therefore, you need to check the composition and recipient exactly at the moment of confirmation in the application.
Will Steam return items after an API scam?
Almost never. Formally, the exchange was confirmed by the account owner, so Valve does not consider this an unauthorized transaction.
How can I tell if I have someone else's API key?
Open steamcommunity.com/dev/apikey. If a key is registered there that you did not create, the account should be considered compromised.
Stolen Steam account: what to do immediately
Order of actions by minute: which device to work from, what to restore first and why mail is more important than Steam itself. Plus that you can actually return it.
Read guide
How to check a Steam link for phishing
How to read a domain from right to left, which Steam addresses are real, how a fake login window differs from a real one, and why a browser lock does not guarantee anything.
Read guide